

Salesforce Authenticator
4.4

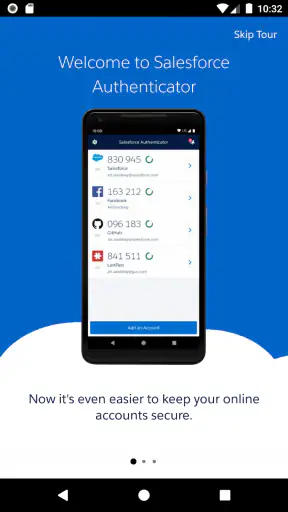
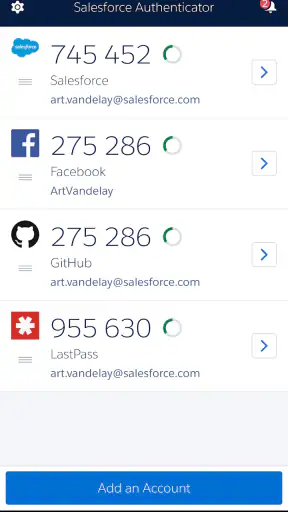
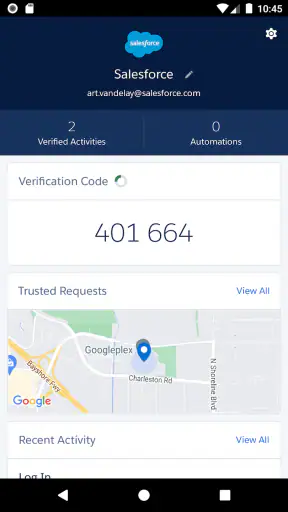
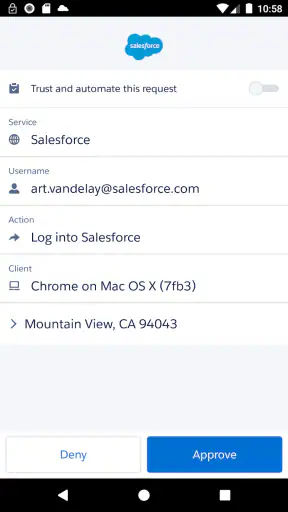
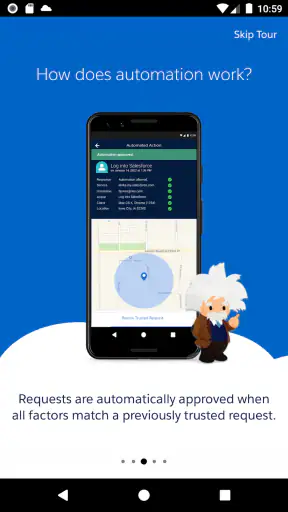
When a household relies on the same business accounts, the awkward part is rarely the password itself. The real problem is deciding who should approve a sign-in, which phone is trusted, and what happens when the person holding that phone is away. I found Salesforce Authenticator most useful in that exact space: it adds a second verification step to supported Salesforce sign-ins, turning the phone into an approval point rather than another place to store a password.
I would not describe it as a general password manager or a family safety tool. It is a focused business security app from Salesforce.com, inc., and its value depends on how your organization has configured Salesforce access. For a small team, a household member who manages a business account, or anyone who wants a clearer boundary between a login and the device approving it, that narrow purpose can be reassuring. For people looking for one authenticator for every online service, the fit is less certain.
How it feels in a shared household
A realistic example is a couple running a small online shop. One person handles orders and customer messages, while the other manages invoices and account settings. They may occasionally use the same Salesforce environment, but they should not casually pass a phone around or make one person permanently responsible for every verification request. The app helps make the approval step visible: the person with the registered device can review the request and decide whether it belongs to a real sign-in.
That distinction matters on a shared device. A phone can be physically available to several people, but the authenticator still represents a particular account relationship. I would treat the device as belonging to the authorized account holder, not as a communal household key. If everyone uses the same phone without an agreed process, the extra security step can become confusing rather than protective.
In my experience, the best household arrangement is simple: one person is the primary owner of the Salesforce identity, and another person has their own properly managed access where the organization allows it. The app should support that boundary, not replace it. Sharing an approval screen may be convenient during a busy day, but it makes later questions harder to answer: who approved the request, why was it expected, and should that device still be trusted?
This is also why I would avoid installing it on a tablet or spare phone merely because several people can reach that device. A device left in a kitchen or home office has a different risk profile from a phone kept with its owner. If the authenticator is going to approve access to customer, sales, or company information, physical access deserves the same attention as the password.
What the app actually adds to a sign-in
The central idea is two-step verification. A password proves that someone knows the account secret; the authenticator adds a separate approval action through the registered phone. That extra checkpoint is especially useful when a password has been reused, exposed, or entered on an untrusted computer. It does not make careless account sharing safe, but it does make an unexpected login easier to notice and reject.
The approval habit is more important than the installation itself. I recommend pausing whenever a request appears and asking whether I just started a Salesforce sign-in. If the answer is no, I would deny it and investigate rather than tapping through automatically. In a household, this small pause prevents a common failure: one person assumes another person initiated the request, and an approval is granted without anyone really checking.
The app is free, which removes an obvious barrier for individuals and small teams. It is rated for Everyone, so its age classification does not make it unsuitable for a family phone on its own. Still, an Everyone rating is not the same thing as a child-friendly account system. The information being protected may be business-sensitive, and the person approving access should understand what the request means.
Setup is easy to start, but boundaries matter
The first decision should not be “which phone is most convenient?” It should be “which person is responsible for this Salesforce account?” Once that is clear, the setup can follow the organization’s sign-in process. I would keep the account owner nearby, use the intended Salesforce credentials, and avoid registering a device that belongs to somebody who may leave the team or stop managing the account.
That sounds obvious, but shared homes create edge cases. A partner may help with administration, a teenager may borrow a parent’s phone, or an older relative may need assistance during setup. In each case, I would separate physical help from account ownership. Helping someone install the app is different from making your own device the permanent approval device for their work identity.
Another practical point is device replacement. Before wiping an old phone, changing the main household device, or handing it to someone else, I would check the organization’s Salesforce sign-in process and plan the transition. Two-step verification is strongest when the registered device follows the legitimate account owner. A forgotten device can turn a routine phone upgrade into an access problem.
The current version is 4.8.0, and the minimum operating system is iOS 9. That makes the app relevant across a wide range of Apple devices, including some older hardware. I would still judge an old phone by its overall security condition, not just whether the app can run on it. An outdated device that is unlocked, shared freely, or rarely updated may be a poor place to approve business access.
One useful setup rule is to write down an internal recovery plan without recording sensitive approval details in an open household notebook. The plan might identify the person who manages the Salesforce account and the administrator to contact if the phone is lost. That is more useful than relying on memory, especially when the primary user is traveling or unavailable.
Coordinating approvals without turning them into a chore
Coordination is where this app either becomes practical or irritating. If two people regularly work in the same Salesforce environment, they should agree on when an approval is expected and how to handle an unfamiliar request. A short message such as “I’m signing in now” can prevent the other person from treating a legitimate notification as suspicious. It also avoids the opposite mistake: approving everything because requests are frequent.
I would not recommend using one person as a permanent human notification service for another person’s account. If the account owner cannot reliably reach the registered phone, the organization should review the account arrangement rather than normalize informal forwarding. The app is designed to strengthen the connection between an account and a trusted device; constant handoffs weaken that clarity.
For a household with occasional shared work, a good routine is to keep the approval device with the account owner and let the other person use their own authorized credentials when possible. For a very small business, this may feel slower than sharing one login, but it gives each person a cleaner responsibility boundary. If someone leaves the project, access can be addressed as an account issue instead of guessing which shared device still has authority.
There is also a useful travel scenario. Suppose the account owner is away and a partner needs to complete an urgent task. The right preparation is not to leave the authenticator on a permanently accessible phone. It is to make sure the partner has the appropriate access before the trip and that the business knows who can help with account recovery. The app can add a verification step, but it cannot create a sensible delegation policy for you.
Notifications can be disruptive when a person is handling several sign-ins in a row, particularly if the phone is being used for ordinary family tasks at the same time. I found that the answer is process rather than blind approval: group legitimate work into a planned session, keep the phone available to its owner, and stop when a request does not match the action just taken.
Age, trust, and the meaning of a shared phone
Because the app’s content rating is Everyone, a family may reasonably install it on a device used around children. I would not, however, give a child responsibility for approving Salesforce access simply because the child knows the phone passcode or can recognize an icon. The important question is judgment. Can the person identify an expected sign-in, understand that an approval grants access, and report a suspicious request?
This becomes especially important when a parent uses a shared iPhone for both work and family life. A child borrowing it to watch videos or make a call may see an approval request at an inconvenient moment. The child should know to leave it alone and alert the account owner. That household rule is more valuable than pretending the device is private when it is not.
Trust should also be reviewed when relationships or responsibilities change. A former employee, housemate, contractor, or family member may once have needed access but no longer should. Removing a person’s access from Salesforce and reviewing registered authentication devices are separate parts of closing that relationship. Keeping the app installed does not automatically solve account administration.
I appreciate that the app’s purpose is narrow because it makes this conversation easier. It is not trying to manage screen time, supervise children, organize family passwords, or coordinate chores. If those are the needs you are trying to solve, a dedicated family-management or password tool will be a better match. Salesforce Authenticator belongs in the security layer of a Salesforce workflow, not in the center of household organization.
Where it beats ordinary alternatives
The usual alternative is relying on a password alone. Against that approach, the app provides a meaningful extra checkpoint, especially for business accounts that contain customer or operational information. The advantage is not that approval is magical; it is that a stolen password is less likely to be enough by itself.
Another alternative is a general-purpose authenticator that generates time-based codes. Those tools can be more flexible when one person wants a single app for many unrelated services. They may also suit users who prefer copying a code rather than responding to a sign-in approval. Salesforce Authenticator is more focused: its appeal is the direct approval experience around Salesforce access, while its usefulness outside that environment is limited.
Text-message verification is often familiar and easy to explain to relatives, but it depends on receiving a message and entering a code. A dedicated authentication app avoids making the phone number the entire second step. I still would not claim that one method is perfect for every account or organization. The better choice depends on the company’s policy, the user’s devices, and how recovery is handled when a phone is unavailable.
The trade-off is convenience versus accountability. A password-only workflow is quicker until something goes wrong. A verification prompt adds a moment of friction every time access needs confirmation, and that moment can annoy people who sign in frequently. In my view, the friction is reasonable for Salesforce accounts with meaningful business consequences, but excessive for someone who only wants a universal code generator for unrelated services.
Everyday strengths and practical friction
The strongest part of the experience is its clarity of purpose. I can explain it to a nontechnical family member in one sentence: this phone helps confirm that a Salesforce sign-in is really yours. That is easier to act on than a complicated security dashboard filled with settings that nobody checks.
Its weakness is the dependency on the trusted device and the surrounding account process. A dead battery, lost phone, changed device, or unavailable owner can interrupt work. That is not a defect unique to this app, but it is a real cost of stronger authentication. Before depending on it for an important operation, I would make sure the organization has a recovery route and that more than one person knows whom to contact.
I also think the app asks for a level of discipline that households do not always have. If everyone taps approvals while distracted, the second factor becomes a reflex instead of a security decision. The best results come from treating each prompt as a question, not as a notification to clear.
With an average rating of 4.4 from around twenty-seven thousand ratings, it has a solid reception, and it has passed five million installs. Those figures suggest that the focused approach works for a substantial audience, but they do not change the central qualification: the app makes the most sense when Salesforce is already part of your work or account environment.
Who should install it, and who should skip it
I would recommend it to Salesforce users who want an additional sign-in check, small businesses that need a straightforward approval workflow, and households where one member manages a Salesforce account without wanting to treat a shared phone as a shared identity. It is also a sensible choice for someone who prefers confirming a request on a phone instead of manually copying authentication codes.
I would skip it if you do not use Salesforce, if you are searching for a password vault, or if your main goal is protecting a wide collection of unrelated services through one universal authenticator. I would also hesitate to make it the center of a shared-device setup where nobody is clearly responsible for the account. In that situation, the problem is organizational before it is technical.
The developer is Salesforce.com, inc., which fits the app’s close relationship with Salesforce sign-in. That relationship is a strength when your workplace or project already uses the platform. It is less compelling if you want an independent authentication tool that remains useful after moving between different services.
Since it is free and intended for Everyone, trying it does not require a purchase decision. The more important commitment is behavioral: choosing the right device, keeping account ownership clear, and teaching household members not to approve requests automatically. Those steps determine whether the app adds real protection or merely adds another icon to a phone.
My household verdict
After looking at it as both a business security tool and a shared-device responsibility, I see Salesforce Authenticator as a good specialist rather than a universal solution. It gives Salesforce sign-ins an extra approval layer and can make suspicious access easier to catch. In a home where work and personal activities overlap, that visible checkpoint is genuinely useful.
My recommendation is to keep the arrangement personal even when the phone is shared: one accountable account owner, one clearly managed authentication device, and a backup plan for travel or loss. Let other household members help with setup or work only through access that is properly assigned to them. That approach preserves the app’s security value instead of turning it into an informal family key.
For Salesforce users, the best reason to install it is not convenience alone; it is the pause between a password and real access. If your household can respect that pause and keep account boundaries clear, the app is a sensible free addition to a business sign-in routine. If you need broad multi-service coverage or family management features, I would choose a different category of tool rather than forcing this focused app to do a job it was not built for.
4.4
1.31K Reviews
Pros
- Push approvals are quick and convenient for frequent Salesforce logins.
- Supports biometric verification on compatible phones for faster access.
- Works with multiple Salesforce accounts on one device.
- Provides backup options when push notifications are delayed.
- Clear login activity helps users recognize unexpected authentication attempts.
Cons
- Requires a compatible mobile device for regular account access.
- Phone replacement can make account recovery more complicated.
- Push approvals depend on an active internet or data connection.
- Some advanced security policies may require administrator configuration.
- Frequent login prompts can become inconvenient for users accessing many accounts.


